
Executive Governance Diagnostic
Decision rights, risk ownership, escalation and board reporting.
Governance and programme assurance
The Governance Meridian helps leadership teams build the governance, risk visibility and delivery discipline that complex programmes need in order to land. Digital, cybersecurity, AI and institutional change.
Based in Kigali. Working across East Africa and remotely.
01 / The problem
The technology is rarely the reason these programmes fail.
They fail in month three. The steering committee has met twice, three decisions are still open, the risk register has a column of team names where there should be people, and nobody can say what evidence would prove a control works.
Governance work rarely fails because nobody knows the framework. It fails because nobody owns the milestone and the evidence has no named custodian. That is the problem this practice was built for.
03 / Engagements
Decision rights, risk ownership, escalation and board reporting.
SOC and MDR governance, incident handling, service performance and third parties.
Where AI is in use, how it is classified for risk, the data behind it, human oversight and monitoring.
Scope, dependencies, risks and issues, suppliers, benefits, and how long decisions are taking.
Accountability, citizen trust, data, cyber resilience and delivery.
Cyber risk, AI oversight, digital trust and third-party accountability, in plain language for the people who have to sign off.
Each ends with findings a board can act on and a ninety day roadmap. Nothing runs open-ended.
04 / Field notes
There is no published baseline for AI and data governance readiness in this region. I am starting one at the 1st ISACA Rwanda Chapter Annual Conference on 5 and 6 October: five questions, about five minutes, around thirty conversations. Everyone who takes part gets their own one-page snapshot back, and the findings will be published here.
Read about the studyISACA Rwanda Chapter Annual Conference, 5 October 2026. On people, awareness, and why security programmes need an owner, a baseline and a target rather than a campaign.
05 / About
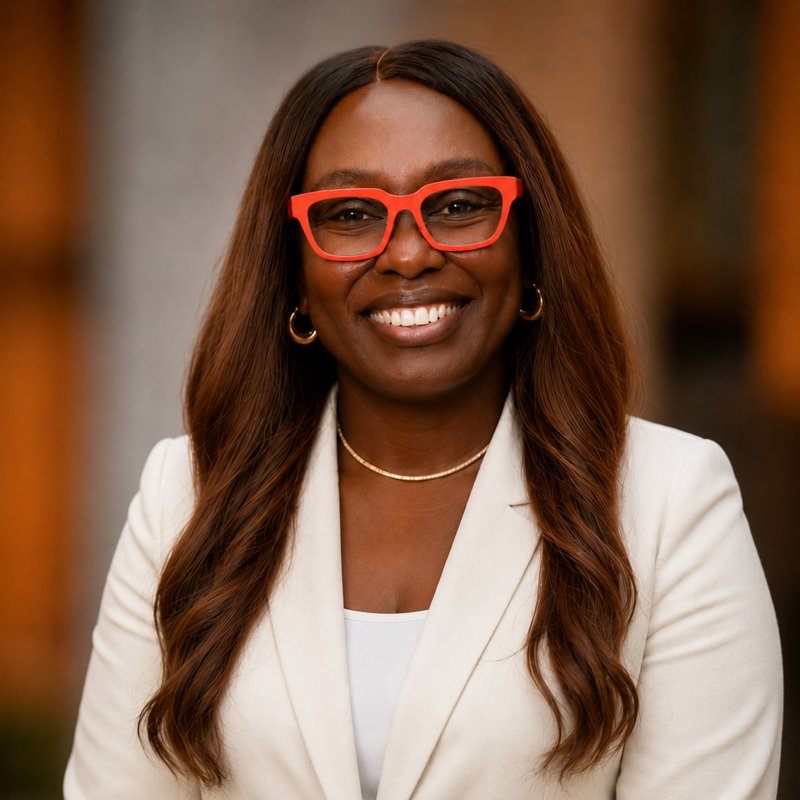
CISM, PMP
The practice is led by Baliyat Johnson, CISM, PMP.
Twenty years running enterprise programmes, the last six in security. At Optiv, she directed cybersecurity engagements worth more than $20M for Fortune 500 managed services clients and built the KPI governance framework that lifted SLA compliance by 40 percent. Before that, $180M+ of wireless infrastructure delivery at MTN Nigeria, where she also designed a Project Management Centre of Excellence adopted across MTN's operating companies. Earlier delivery work at AT&T.
The through line is delivery discipline: getting the right decision made by the right person, on a date, with the evidence to show for it.
She moved to Kigali from Denver in August 2026, so she is new to this market and says so. The method is not new. The picture of what is true here is still being built, and she would rather ask than assume.
07 / Contact
If a programme you are responsible for is complex enough that you are not sure who owns what, that is usually the right time to talk.
Your details are stored with our website provider, Lovable Cloud, on servers in the United States. We use them only to reply to you, and delete them on request to advisory@governancemeridian.com.